
Notes on AI agent security.
Research and analysis on AI agent security, threat modeling, prompt injection, and vulnerability patterns we see in the wild.
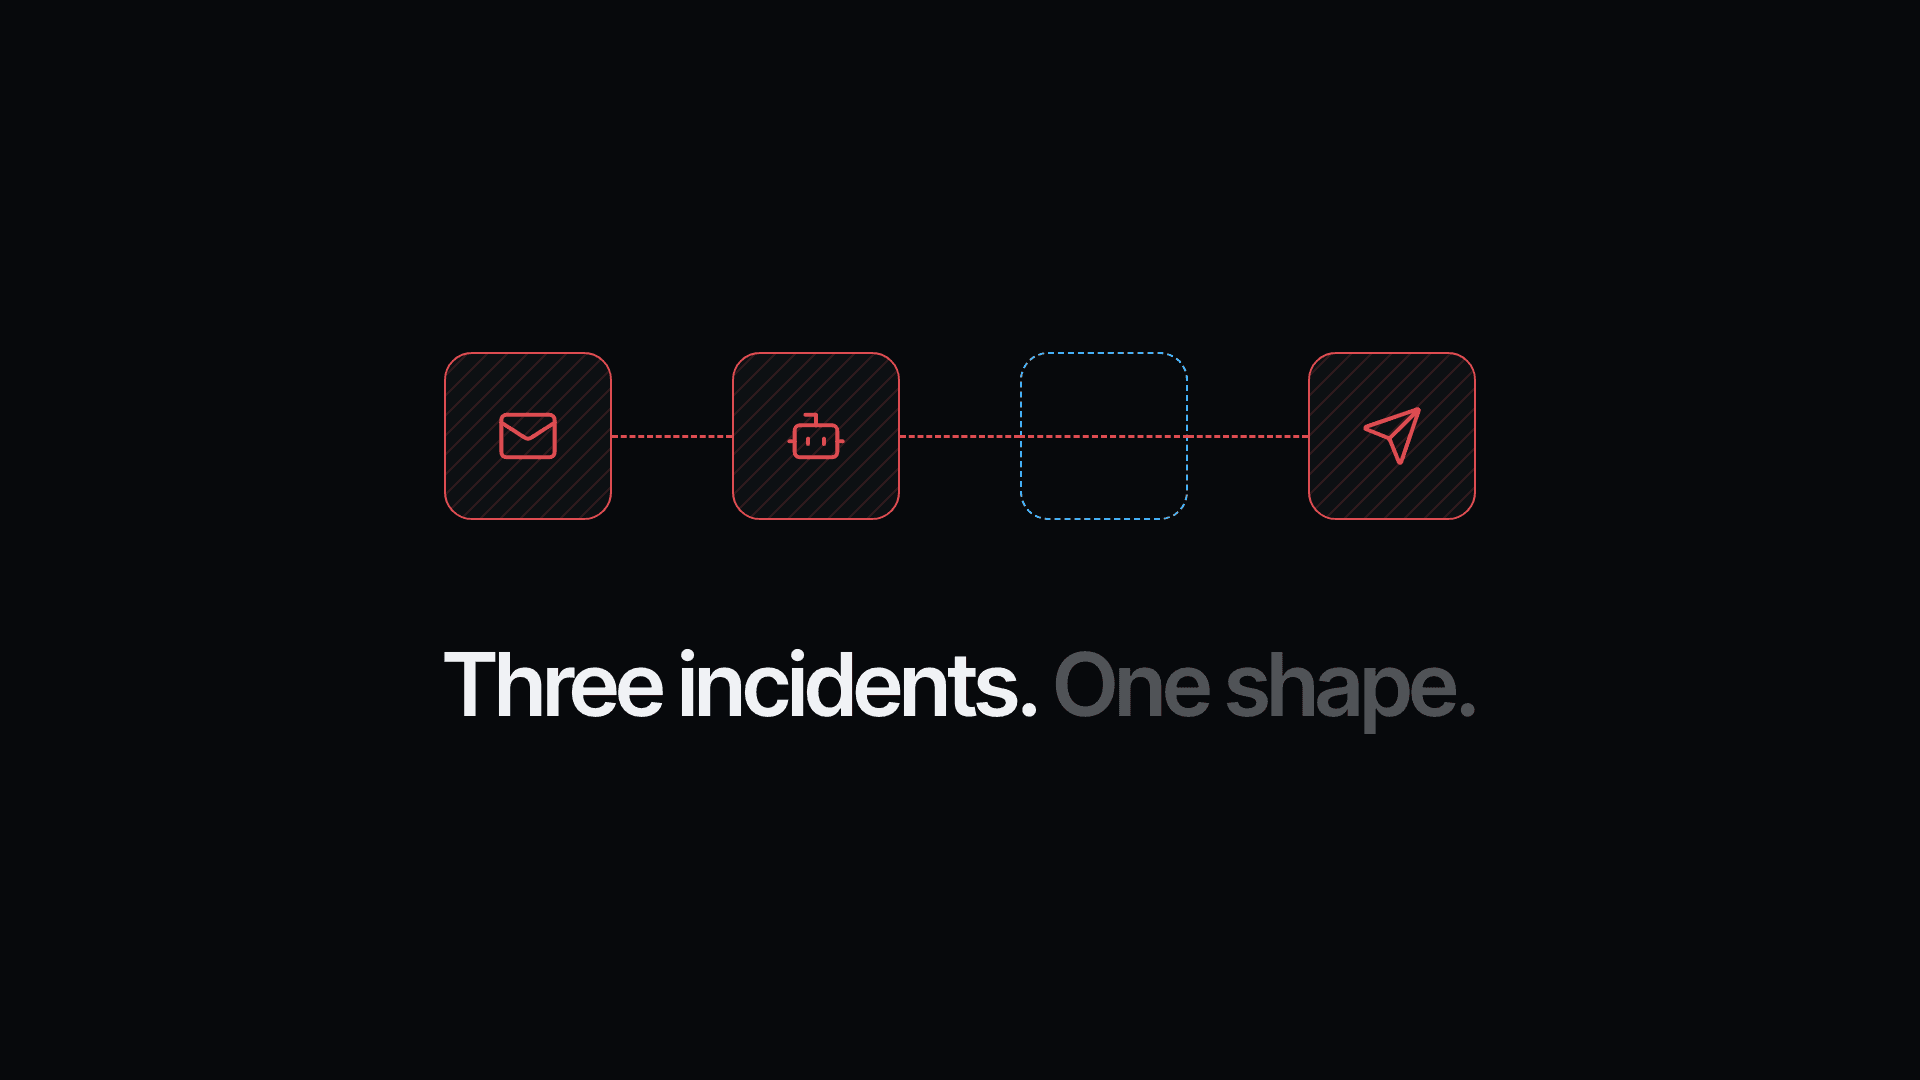
The permission checks were working. The data left anyway.
EchoLeak, the Slack AI leak and the Supabase MCP leak, rebuilt on a canvas. Same five boxes, same missing node.
Agents, Leaks & Regulations
The gap between AI adoption and AI security is widening fast. Here's what companies are getting wrong and what to do about it.
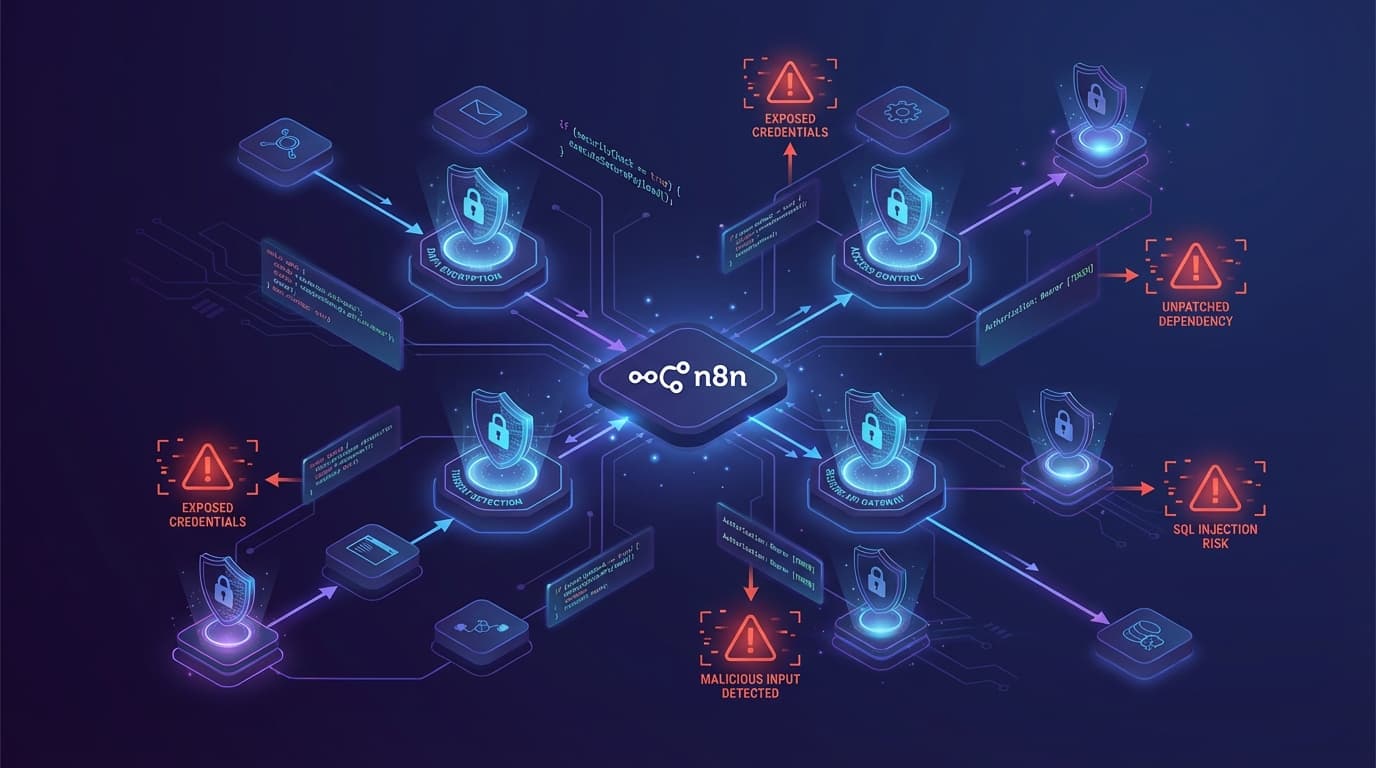
Security Risks in n8n Workflows: A Practical Guide
A comprehensive guide to understanding and mitigating security vulnerabilities in n8n workflows, covering CVEs, code execution risks, webhook security, and infrastructure hardening for self-hosted deployments.

Claude Goes to War: Inside China's GTG-1002 Autonomous Cyberattack
How a Chinese state-sponsored group used Claude Code to autonomously execute the first documented large-scale AI-driven cyberattack against 30 global targets, achieving what was previously impossible for human operators.